Opening a digital storefront and expanding your traditional business to reach global customers is an exhilarating milestone. However, it comes with a sobering reality: cybercriminals actively scan the web looking for vulnerable, non-technical small businesses that lack enterprise-grade security defenses.
Many traditional retailers and service providers migrating online deeply underestimate their digital attack surface, mistakenly assuming hackers only target massive financial institutions or global corporations. In reality, automated botnets attack small e-commerce sites around the clock. By implementing foundational cybersecurity protocols, secure payment gateways, and everyday employee hygiene practices, non-tech businesses can safely scale their online operations and protect hard-earned customer trust.
Understanding the E-Commerce Threat Landscape
Before securing your digital storefront, it helps to understand the specific ways malicious actors target online businesses. Familiarizing yourself with these common threats is the first step toward defense:
- Payment Interception and Skimming: Hackers routinely inject malicious JavaScript scripts into vulnerable checkout pages to silently harvest customer credit card numbers and personal details as they are typed.
- Phishing and Business Email Compromise (BEC): Deceptive, highly targeted emails sent to employees or owners designed to steal login credentials, trick staff into wiring funds, or gain unauthorized access to administrative dashboards.
- Ransomware and Data Extortion: Malicious software that infiltrates your network and locks down critical inventory management systems, customer databases, or accounting files until a steep financial ransom is paid.
- DDoS (Distributed Denial-of-Service) Attacks: Overwhelming floods of artificial traffic designed to crash your online store precisely during peak shopping seasons or major promotional events.
Core Cybersecurity Foundations for Online Storefronts
You do not need to be a software engineer to secure your website. Choosing the right foundational architecture does much of the heavy lifting for you:
- Choosing Secure E-Commerce Platforms: Opt for reputable, managed e-commerce solutions (such as Shopify, BigCommerce, or well-maintained WooCommerce setups) rather than custom, brittle builds. These platforms handle core infrastructure security, automated security patches, and threat monitoring.
- SSL Certificates and Encrypted Data: Ensure your website uses robust HTTPS encryption across every single page—not just the checkout. This secures data in transit between your customers and your server.
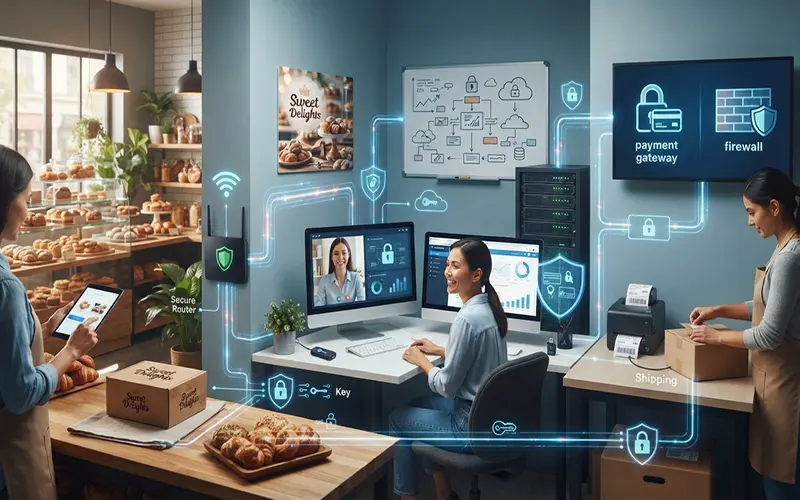
- PCI-DSS Compliance: The Payment Card Industry Data Security Standard is mandatory for anyone handling card data. The easiest way for non-tech businesses to comply is to outsource credit card processing entirely to trusted payment gateways (like Stripe, PayPal, or Apple Pay), keeping card numbers off your own servers.
- Automated Regular Backups: Set up automated, off-site, and immutable daily backups. If your site is ever compromised by malware or data corruption, a clean backup allows you to restore operations in minutes without paying a ransom.
Operational Hygiene and Employee Security Training
Technology alone cannot protect your business; human habits are frequently the weakest link in digital security. Establishing strong operational hygiene is vital:
- Mandatory Multi-Factor Authentication (MFA): Enforce MFA across all administrative dashboard logins, business email accounts, and financial portals. MFA blocks the vast majority of automated password-stuffing attacks even if a password is leaked.
- Role-Based Access Control (RBAC): Give employees, freelance contractors, and third-party marketing vendors only the minimum system permissions necessary to do their specific jobs, limiting exposure if an account is compromised.
- Security Awareness Training: Educate non-tech staff on how to spot convincing phishing scams, recognize suspicious customer service inquiries, and use secure password managers instead of writing credentials on sticky notes.
Incident Response: What to Do When Things Go Wrong
Even with robust preventative measures in place, no business is entirely immune to security incidents. Having a basic, written disaster recovery plan prepares you to act swiftly if something feels wrong.
Your incident response plan should clearly outline who to contact, how to temporarily isolate compromised systems from the internet to prevent lateral spread, and who to notify among stakeholders, customers, and legal or IT support partners.
Robust cybersecurity is not just a tedious IT expense or a technical checkbox; it is the ultimate foundation of customer trust and business longevity online.
By taking proactive steps to secure your payment gateways, enforce multi-factor authentication, and train your team, you can build a resilient e-commerce presence that thrives securely in the digital economy.